Understanding the Roles
The primary difference between a cybersecurity analyst and a cybersecurity engineer is that analysts oversee networks to identify and prevent data breaches, whereas engineers design and implement security architecture and solutions. CompTIA outlines this functional split as the baseline for dividing operational monitoring from infrastructure creation.
 TechMediaArch.com |
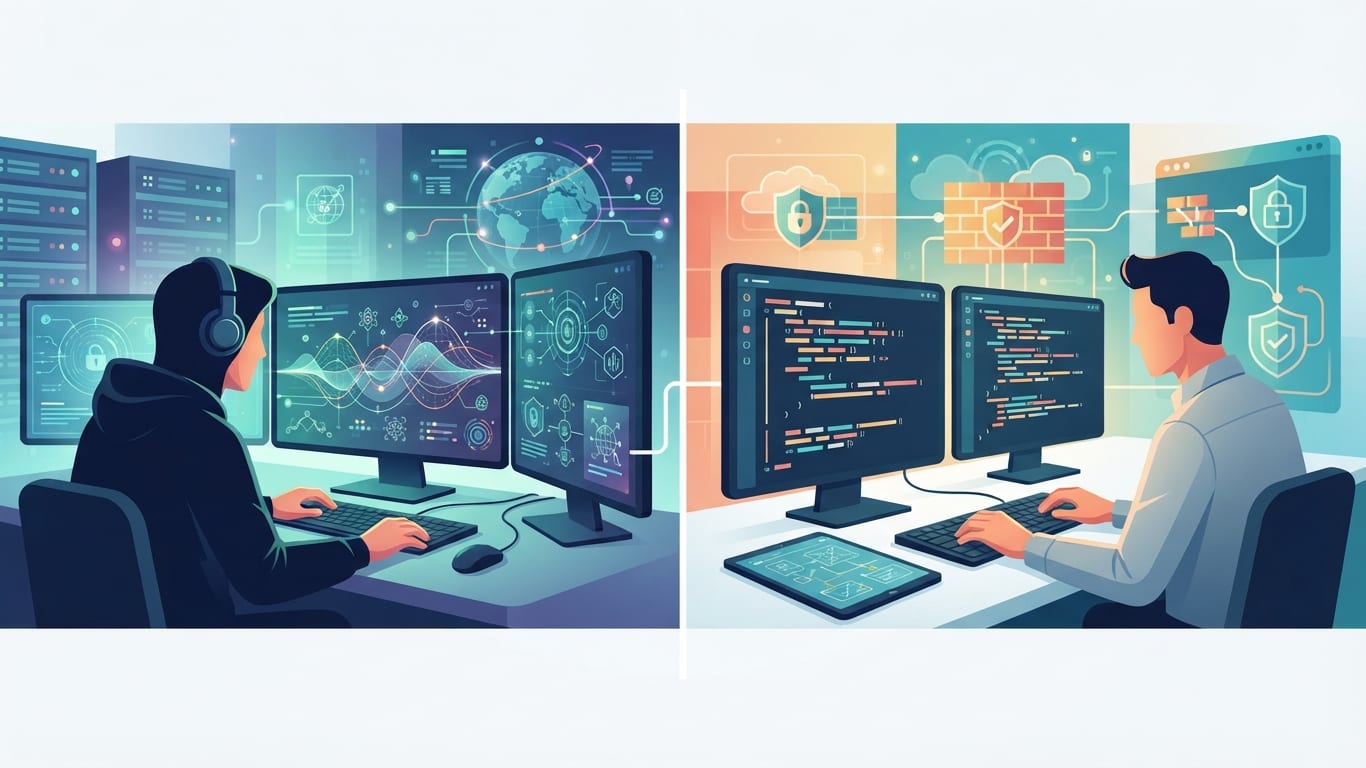
| Split illustration comparing cybersecurity analyst monitoring and engineer building |
According to Discover Data Science, cybersecurity engineers focus primarily on building systems, while cybersecurity analysts focus on identifying problems within those existing systems so they can be improved.
Analysts evaluate network traffic and scan parameters to spot abnormalities before they escalate into full-scale compromises. Engineers construct the underlying frameworks that make those security measures structurally possible across enterprise networks.
Without analysts reviewing daily logs, vulnerabilities remain hidden until exploitation occurs. Without engineers building resilient code and network segments, analysts lack the necessary barriers to block malicious actors.
Budget allocations often reflect this functional split by dividing resources between detective controls and preventative engineering. Technical directors assign engineers to development phases and analysts to operational phases.
Core Responsibilities of a Security Analyst
The U.S. Bureau of Labor Statistics notes that an information security analyst carries out several key responsibilities:
- Plans, implements, upgrades, and monitors security measures for the protection of computer networks and information
- Assesses system vulnerabilities for security risks
- Proposes risk mitigation strategies
- Ensures appropriate security controls are in place to safeguard digital files and vital electronic resources
Skill IT Education reports that a cybersecurity analyst handles a wider remit that typically includes vulnerability management, risk assessment, security controls, and compliance, usually working during standard business hours. Analysts evaluate ongoing operational posture rather than building foundational code or physical infrastructure.
Daily routines involve reviewing scanner outputs, auditing user permissions, and verifying that endpoint protection agents remain active. Analysts review reports from automated tools to determine if discovered weaknesses require immediate patching or compensating controls.
When third-party vendors introduce new software, analysts examine the associated risk profiles before deployment. They collaborate with system administrators to apply patches that address newly discovered zero-day exploits or common vulnerabilities.
Documentation forms a major part of the analyst workload, requiring detailed records of security control audits and risk assessments. These reports provide executive leadership with the metrics needed to make informed security investments.
What Does a Cybersecurity Engineer Do
According to CISA, cybersecurity engineering under the NICE framework involves working within engineering departments to design and create systems, processes, and procedures that maintain the safety, reliability, and security of industrial systems against cyber events. Engineers construct the actual defenses that protect digital assets from external intrusions.
Indeed explains that cybersecurity engineers learn about changes to government regulations and update existing systems or build completely new ones to ensure compliance. Security analysts monitor systems without holding primary responsibility for government regulation compliance.
Professionals in these engineering tracks often build robust defenses, with mid-to-senior roles earning base salaries between $110,000 and $165,000, while specialized certifications like the CISSP push pay higher, according to KORE1 data.
Engineers integrate firewalls, intrusion prevention appliances, and encryption protocols directly into the network topology. They write custom scripts to automate security configuration management across cloud environments and physical data centers.
When new legislative mandates take effect, engineers modify system architecture to satisfy statutory requirements. They test these newly engineered defenses against simulated attack vectors to confirm structural integrity before production release.
Analyst Versus SOC Operations
A Reddit community discussion on r/cybersecurity points out that a cybersecurity analyst works primarily on the risk, compliance, and preventative side, whereas a SOC analyst operates closer to the incident response and real-time detection side. The daily routine of an analyst differs substantially from frontline defenders.
SOC Masters details that a SOC analyst works inside a Security Operations Center monitoring SIEM alerts in shifts to triage, investigate, and respond to incidents in real time, contrasting with the broader vulnerability and compliance focus of a cybersecurity analyst. Shift work is common in a Security Operations Center because threats emerge around the clock.
Skill IT Education clarifies that a SOC analyst's day-to-day work centers on live alert queues, log analysis, and threat detection dashboards. Meanwhile, a cybersecurity analyst maintains a broader role spanning risk assessment, policy development, and security control audits.
SOC analysts stare at monitoring screens watching for indicators of compromise generated by security information and event management platforms. When a high-severity alert fires, the SOC analyst must isolate the affected host immediately.
General cybersecurity analysts rarely sit in these live triage queues during off-hours shifts. Instead, they focus on long-term preventative measures such as refining corporate security policies or conducting risk assessments for upcoming software rollouts.
 TechMediaArch.com |
| Minimalist graphic showing security shield in a digital network |
Cybersecurity Versus Software Engineering
Boise State University explains that cybersecurity involves protecting computer systems, networks, and data from theft, unauthorized access, and damage, whereas software engineering is the process of coding, designing, and maintaining software applications and systems. These technical tracks require distinctly different educational backgrounds and daily skill sets.
UWA Online reports that software engineers build the systems, applications, and platforms that power modern organizations, while cybersecurity professionals protect those systems from emerging digital threats and vulnerabilities. As organizations deploy complex architectures, developers and defenders must coordinate to mitigate risks outlined in resources like What Are Zero Trust Security Models: A Complete Guide.
Destination Certification defines the core mission distinction by noting that software engineers build the future of technology, while cybersecurity professionals ensure that this future remains secure.
ONLC adds that software engineering focuses on developing and maintaining software through the software development life cycle, whereas cybersecurity prioritizes protecting programs, systems, and data using security tools and protocols.
Software engineers write functional code that implements business logic, user interfaces, and database interactions. Cybersecurity professionals analyze that exact code for injection flaws, buffer overflows, and insecure direct object references.
Development teams prioritize feature delivery and execution speed within strict product timelines. Security teams prioritize reducing attack surfaces and enforcing strict access controls, occasionally creating friction between operational goals.
Compensation and Career Outlook
The median annual wage for information security analysts was $129,180 in May 2025, according to the U.S. Bureau of Labor Statistics. Herzing University notes that the average salary for information security analysts positions them competitively among IT roles, with mid-to-senior levels scaling higher based on experience and education.
Indeed reports that the national average salary for a cybersecurity analyst is $87,876 per year, with geographic location, professional experience, and technical knowledge heavily influencing total compensation.
Analysts and engineers alike see compensation adjust upward as they acquire specialized operational responsibilities or manage incidents similar to those discussed in What Are Phishing Emails and How Do Cyberattacks Work?. Engineering roles typically command higher baseline compensation due to the technical complexity of designing secure infrastructure from scratch.
Frameworks and Standards
The NIST Cybersecurity Framework provides a structured approach consisting of functions, categories, and subcategories to help organizations manage cybersecurity risk and build operational security cultures. Engineers and analysts incorporate these standard guidelines into daily operations to secure networks against attacks.
Engineers use framework subcategories to verify that all necessary hardware and software controls are built into new system architectures. Analysts reference these same standards when auditing existing operational procedures for compliance gaps.
Key Differences at a Glance
Comparing these technical disciplines highlights the distinct operational focuses required across modern IT departments:
- Analysts oversee networks and identify vulnerabilities, while engineers design and build security architecture.
- Engineers handle regulatory compliance updates for systems, whereas analysts monitor environments without primary compliance ownership.
- Software engineers build applications through the development life cycle, while security professionals protect those assets.
- SOC analysts monitor live alert queues in shifts, whereas cybersecurity analysts handle broader risk and policy duties during standard hours.
FAQ
What does cybersecurity analyst do
An information security analyst plans, implements, upgrades, and monitors security measures for the protection of computer networks and information. They assess system vulnerabilities for security risks, propose risk mitigation strategies, and ensure appropriate security controls are in place to safeguard digital files and vital electronic resources.
How much does cybersecurity analyst make
The median annual wage for information security analysts was $129,180 in May 2025 according to the U.S. Bureau of Labor Statistics. Individual pay varies based on geographic location, professional experience, technical knowledge, and organizational level.
What is cybersecurity engineering
Cybersecurity engineering involves working within engineering departments to design and create systems, processes, and procedures that maintain the safety, reliability, and security of industrial systems against cyber events. Engineers build the underlying security architecture and update systems to ensure compliance with government regulations.
What is the difference between cybersecurity analyst and soc analyst
A cybersecurity analyst works primarily on the risk, compliance, and preventative side, handling vulnerability management and policy development during standard business hours. A SOC analyst operates inside a Security Operations Center monitoring SIEM alerts in shifts to triage, investigate, and respond to real-time security incidents.
What is the difference between cybersecurity and software engineering
Software engineering is the process of coding, designing, and maintaining software applications and systems through the software development life cycle. Cybersecurity involves protecting those computer systems, networks, and data from theft, unauthorized access, and damage using specialized security tools and protocols.